AI Act Shield by iaCiao
Local-first redaction and restore of sensitive data, for law firms, accountants and consultants.
Do your associates paste contracts and financial statements into ChatGPT or Claude? Are you really compliant with the EU AI Act and the GDPR?
87% of professional firms share confidential text containing tax IDs, IBANs, names and amounts with the cloud servers of generative AI every day. Sending data in the clear to servers outside the EU is a direct breach of Art. 32 GDPR and of Regulation (EU) 2024/1689.
No governance of input data and non-compliant use in the workplace.
Unlawful transfer outside the EU and failure to apply Art. 32 security measures.
Insurers refuse to pay out when no anonymisation was in place beforehand.
A partner or a trainee pastes a 15-page Word file into ChatGPT — a defence brief or a draft of an extraordinary financial statement — to get a quick summary. The document contains tax IDs, VAT numbers, bank statements with IBANs and details of tax disputes.
- •Data leaked into cloud logs: indexed and retained for 30+ days on servers in the US.
- •Mandatory breach notification: every client must be told, with serious reputational damage.
- •Only anonymisation cures it: an Enterprise account does not cure a transfer in the clear that has already happened.
How AI Act Shield works (local anonymizer, zero cloud)
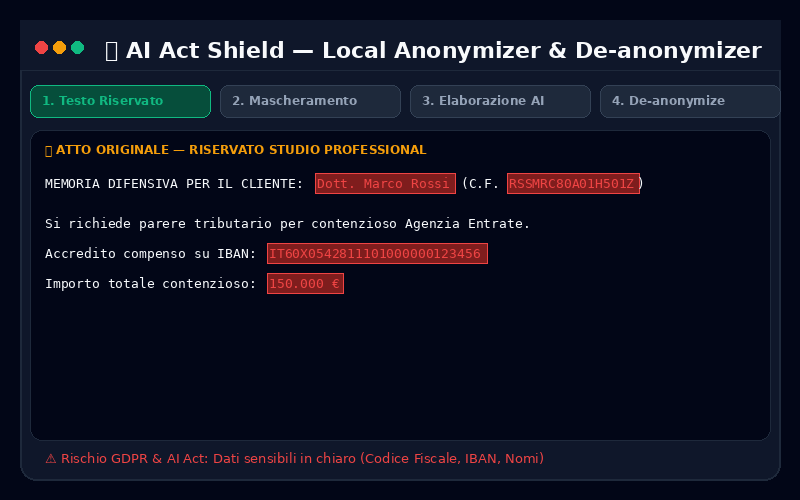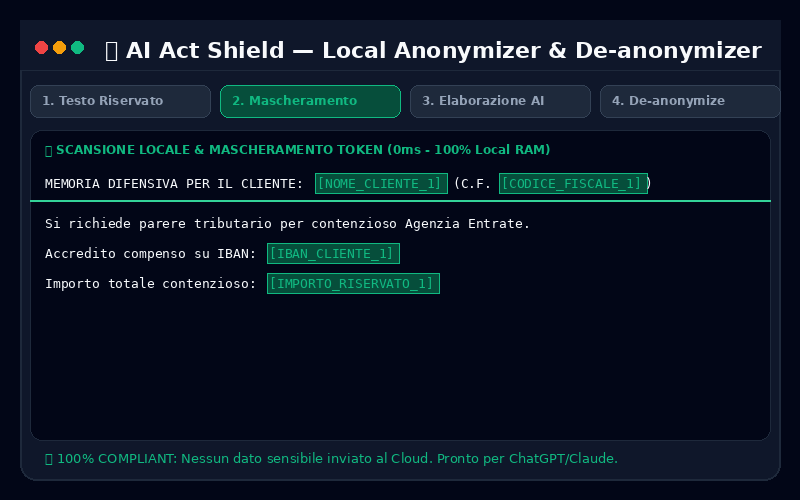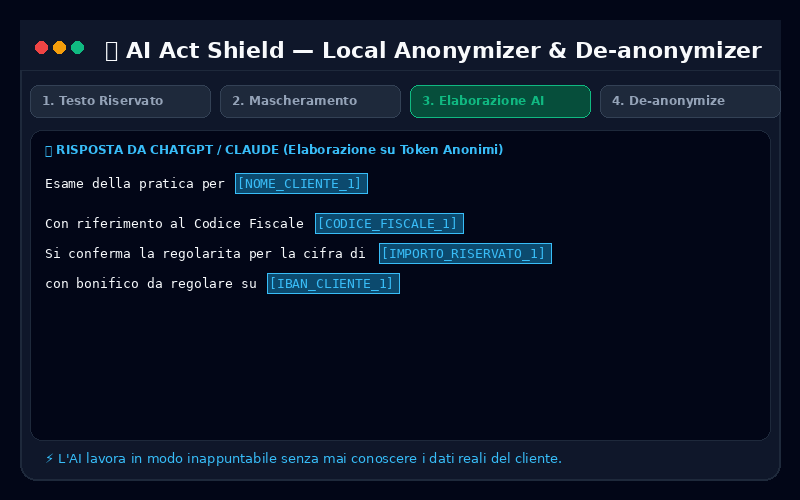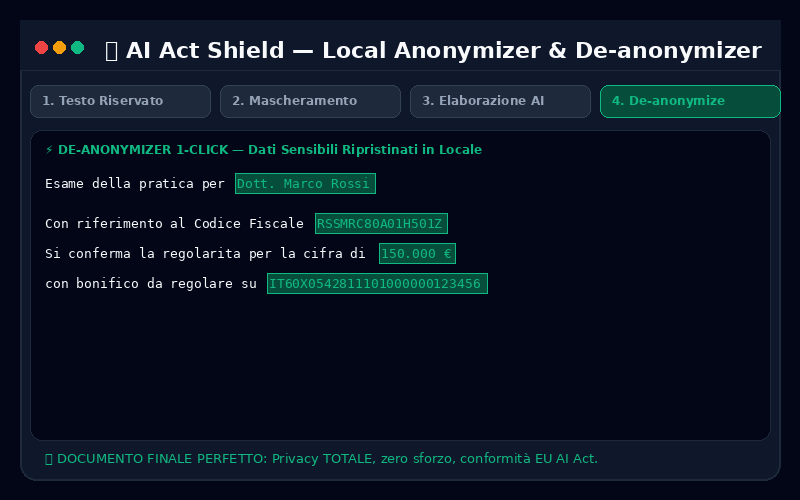
Upload the document or paste the text. The local engine finds and replaces tax IDs, VAT numbers, IBANs and names with anonymous placeholders ([CLIENT_1], [IBAN_1]).
Safely send the masked text to ChatGPT, Claude or DeepSeek. The AI works on the placeholders, and the answer keeps its formal and legal accuracy intact.
Paste the answer back into AI Act Shield: the real data, held in your own computer's memory, goes back into place instantly.
Evaluation matrix for the Managing Partner and the DPO
| Security and compliance criterion | AI used directly (no Shield) | With AI Act Shield (iaCiao) |
|---|---|---|
| Processing of client personal data | ❌ Clear data on US/China servers | ✅ Masked locally, 100% |
| Compliance with Regulation (EU) 2024/1689 | ❌ Penalties up to €35M | ✅ Compliant |
| Adequacy of technical measures (Art. 32 GDPR) | ❌ Penalties up to €20M | ✅ Appropriate technical measures |
| Audit trail certificate for DPOs and inspectors | ❌ Impossible to produce | ✅ Printable in one click |
| Standalone desktop mode (air-gapped) | ❌ Cloud web only | ✅ Offline .EXE / .DMG app |
Automatic detection of tax IDs, VAT numbers, IBANs, professional titles, names, addresses, phone numbers, emails and any confidential term you add yourself.
No document is ever sent to an external server — not even to ours. Masking and restoring happen only in your own computer's memory.